NexusRM / Security and deployment

Your network. Your directory. Your rules.

Role-based access enforced on every endpoint, sign-in through your directory, and a deployment that never needs to reach the internet.

01 / Roles

Admin, Editor, Viewer.

Users hold a global role and can be granted a different role per project. Every API endpoint checks it on the server, so the browser is never the only line of defence. Users only see projects they have been given access to.

  • Admin / Editor / Viewer roles
  • Project-scoped grants
  • Enforced server-side on every endpoint
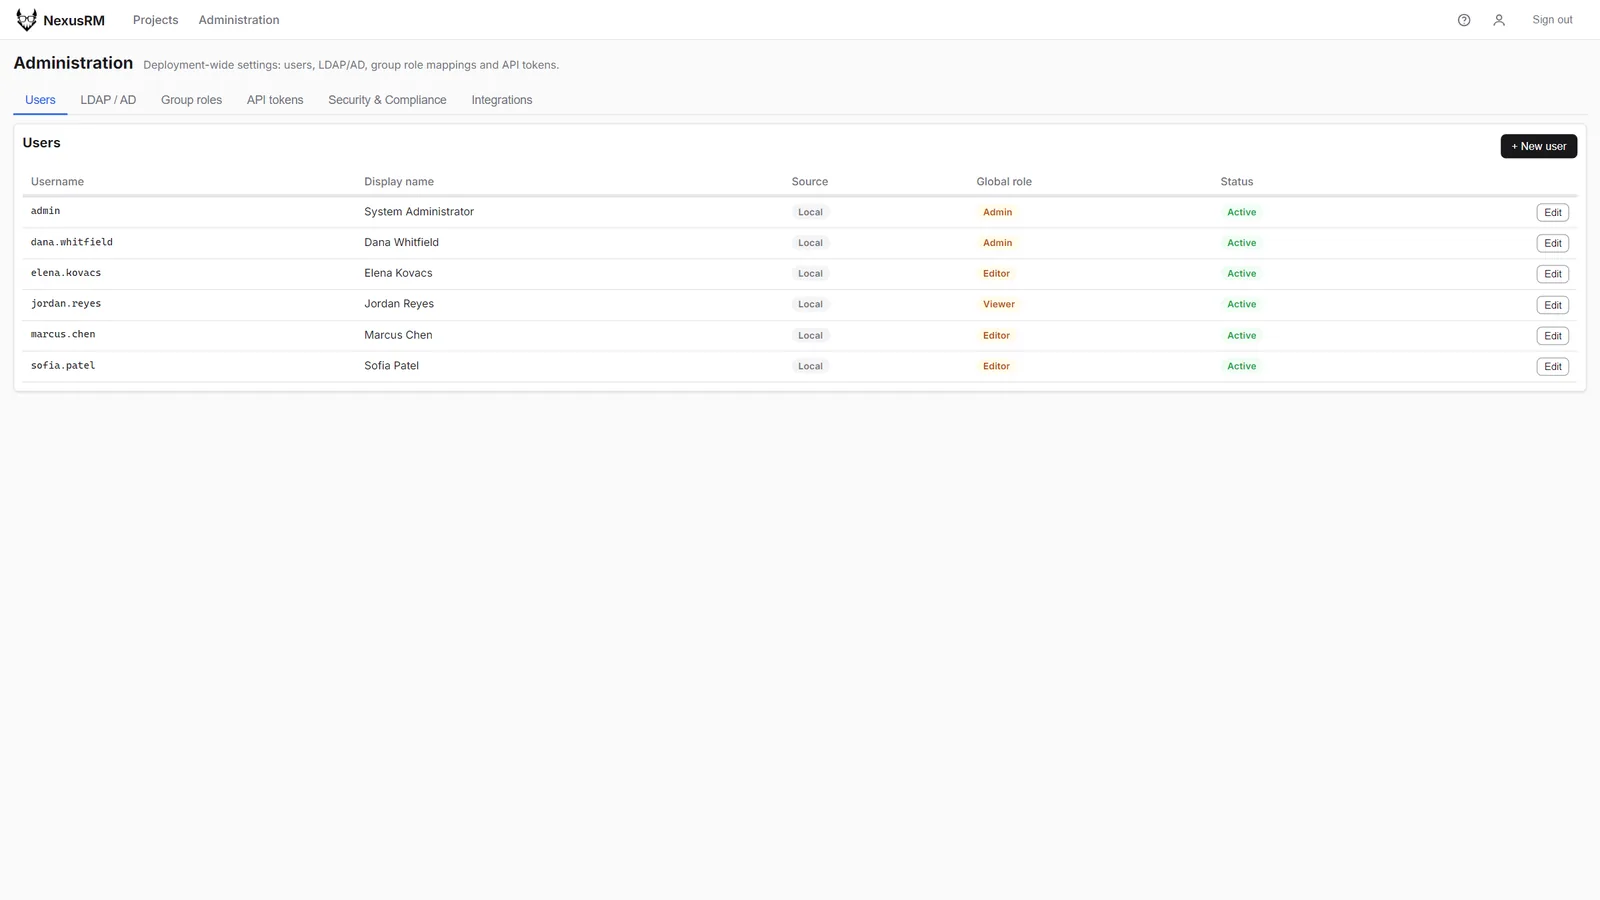
User administration listing users with their Admin, Editor and Viewer roles and account status
02 / Directory

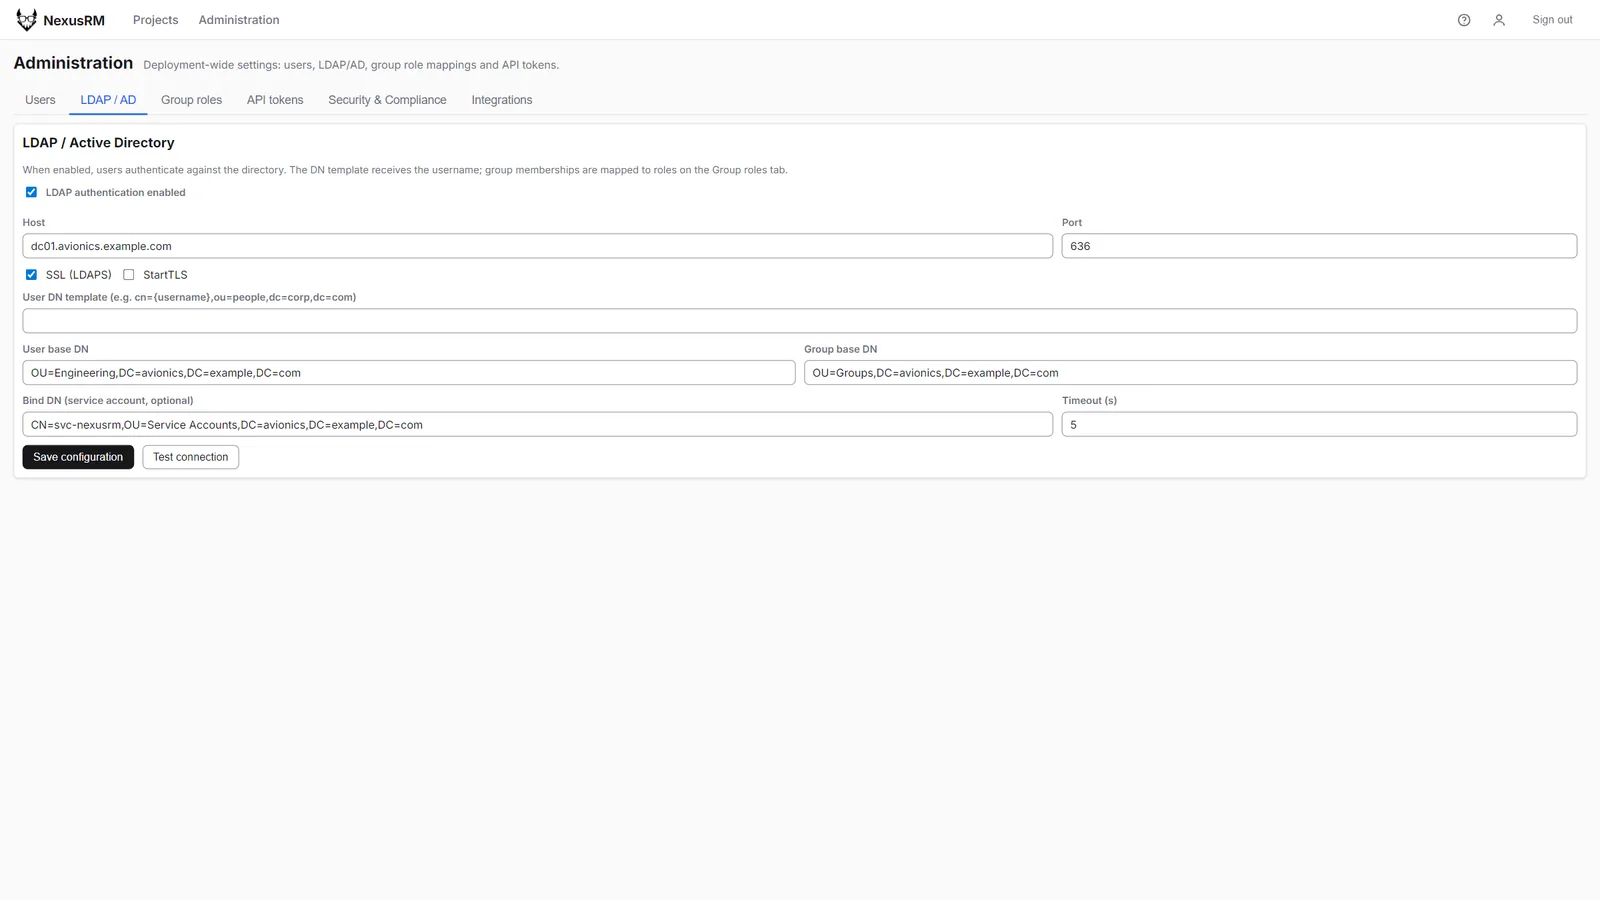
LDAP and Active Directory.

Connect to your directory with LDAPS, base DNs and a bind account, configured in the admin UI and applied without a rebuild. Local accounts remain available for a bootstrap administrator, with passwords hashed using Argon2id.

  • LDAP and Active Directory sign-in
  • Runtime configuration in the admin UI
  • Argon2id for local passwords
LDAP and Active Directory configuration with LDAPS, base DNs and the bind account
03 / Group mapping

Roles from directory groups.

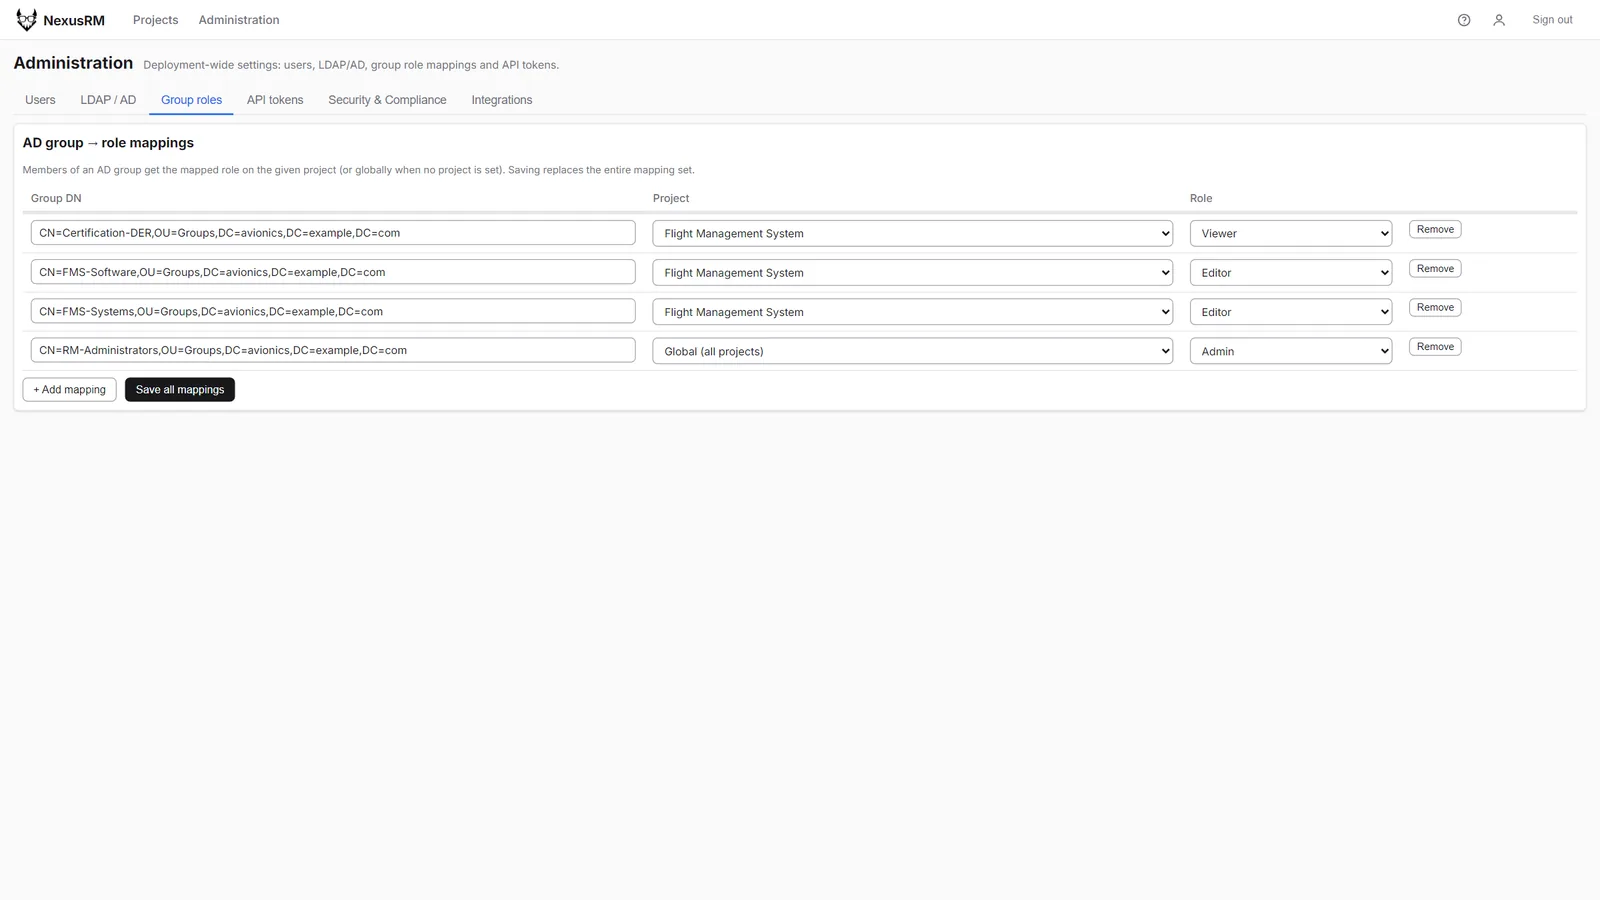
Map directory groups to global roles or to roles on a specific project. Grant access by directory group rather than user by user.

  • Group-to-role mappings
  • Global or project scope
  • Managed in the admin UI
Directory group to role mappings, some global and some scoped to a single project
Deployment

One Docker Compose stack

The application and PostgreSQL 16 in a single-node Compose stack. Migrations apply automatically on first start.

Air-gapped

Zero runtime egress

The frontend is fully bundled and nothing calls out. Images move onto the isolated network with docker save and docker load.

TLS

Behind your reverse proxy

Put your existing reverse proxy in front for TLS termination and certificates.